
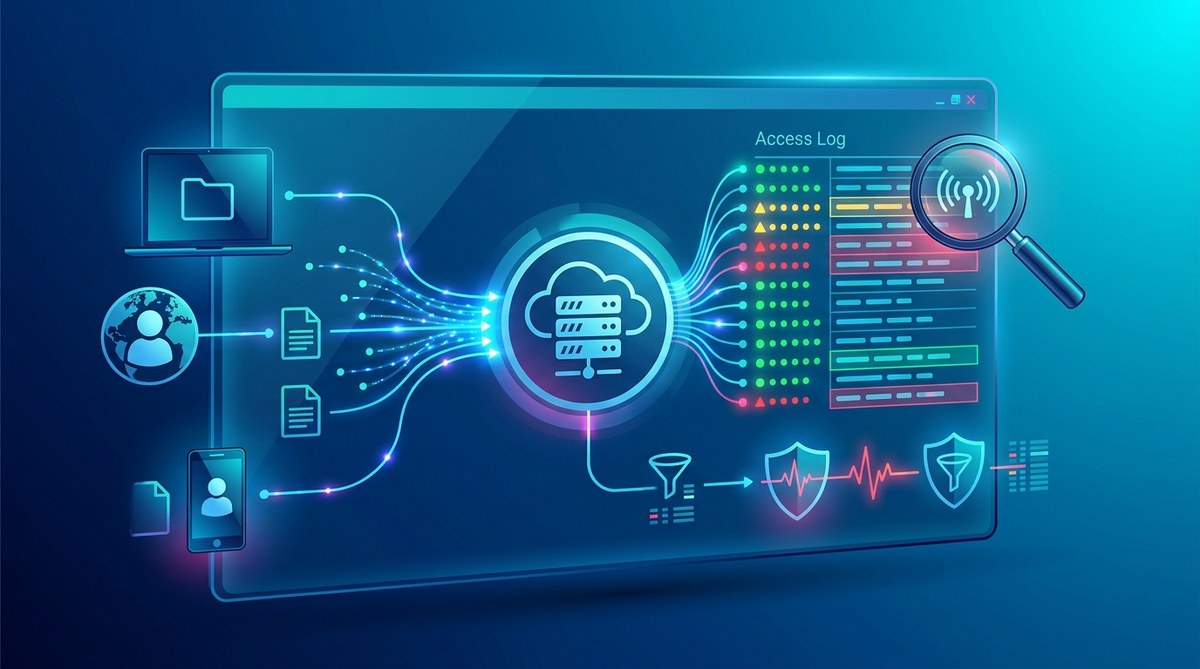
Your file hosting platform is a black box until you look inside. Every download, every failed upload attempt, every suspicious IP that pokes at your storage endpoints leaves a mark in your access logs. For security engineers and DevOps professionals in 2026, those logs are not just a compliance checkbox. They are your early warning system for data exfiltration, brute force attacks, and insider threats.
The hard truth is that most teams collect logs but never truly monitor them in real time. They store terabytes of data and only look back after a breach. That reactive approach costs companies millions every year. But with the right pipeline, you can turn your file hosting access logs into a live security radar that alerts you the moment something looks wrong.
Real-time monitoring of file hosting access logs is your best defense against data breaches in 2026. By aggregating logs from your storage layer, normalizing them into a structured format, and feeding them into a SIEM or alerting engine, you can detect anomalies like credential stuffing, mass downloads, and geo-anomalies within seconds. This guide walks you through the full implementation.
Why Access Logs Are Your First Line of Defense
File hosting access logs capture the who, what, when, and where of every interaction with your stored files. Unlike application logs that may only record frontend activity, access logs give you a raw view of your storage layer. They show you direct API calls, S3 bucket requests, CDN edge hits, and direct download links.
When you monitor these logs in real time, you gain the ability to spot patterns that indicate a compromised credential or a malicious insider. A single user downloading 500 files in two minutes looks very different from normal behavior. An IP address from a country where you have no customers trying to access a sensitive document is a red flag. Without real-time monitoring, these events disappear into the noise of daily operations.
How to Build a Real-Time Log Pipeline
Setting up real-time monitoring for your file hosting access logs takes a few deliberate steps. Here is a numbered breakdown of the process that works for most cloud-native setups in 2026.
-
Centralize your log sources. Start by streaming all access logs from your file hosting layer into a single aggregator. If you use S3-compatible object storage, enable access logging at the bucket level. If you run your own server, configure syslog or a log shipper like Fluentd to forward every request. Do not filter anything at this stage. You want the raw data.
-
Normalize and parse the logs. Raw logs are messy. They come in different formats depending on whether they come from NGINX, an S3 gateway, or a CDN. Use a log parser (like Logstash or Vector) to extract fields: timestamp, source IP, user agent, file path, HTTP method, status code, and file size. Normalize these fields into a consistent schema so your detection rules work across all sources.
-
Stream logs to a real-time analytics engine. Send your normalized logs to a system that can process them in near real time. Elasticsearch with a Kibana dashboard works well. So does a cloud SIEM like Splunk or a lighter solution like Grafana with Loki. The goal is to have data available for query within seconds of the request happening.
-
Write detection rules. This is where the security magic happens. Define rules that trigger alerts. For example, alert if a single IP downloads more than 50 files in 60 seconds. Alert if a download request comes from a geolocation outside your allowed regions. Alert if the user agent string is empty or matches known malicious patterns.
-
Set up automated response actions. Do not just send an email. Configure your pipeline to take action. Block the IP at the edge firewall. Invalidate the user session. Rate-limit the endpoint. The faster you respond, the less damage a compromised key can do.
What to Scan For in Real Time
Your monitoring system is only as good as the signals you ask it to look for. Here is a bulleted list of the most important patterns to scan in your file hosting access logs.
- Mass download events from a single IP address or user token
- Repeated 401 or 403 errors indicating credential stuffing
- Access attempts to files that do not exist (directory traversal probes)
- Requests from unexpected geographic regions
- Unusual download times, such as 3 AM activity from a user who normally works 9 to 5
- User agent strings that do not match known browsers or SDKs
- Requests for files that have not been accessed in months (archival data fishing)
- Repeated attempts to access the same file with different tokens (session replay)
These patterns cover most common attack vectors against file hosting infrastructure. Tune your rules to your normal traffic baseline. If your users are global, geo-fencing may not work for you, but you can still flag rapid changes in location for the same user.
Common Mistakes That Break Your Monitoring
Even a well-designed pipeline can fail if you make these errors. The table below outlines the most frequent mistakes and how to fix them.
| Common Mistake | Why It Hurts | How to Fix It |
|---|---|---|
| Logging only successful requests | You miss reconnaissance attempts and failed brute force attacks | Log all HTTP status codes, especially 4xx and 5xx |
| Not rotating log storage | Your aggregator runs out of disk and stops ingesting new data | Set log retention policies and use cloud object storage for archives |
| Ignoring CDN logs | Direct edge cache hits bypass your origin server logs | Enable CDN logging and forward those logs to your aggregator |
| Using static thresholds | Your rules trigger false positives during legitimate traffic spikes | Implement adaptive baselines that learn from historical patterns |
| No field normalization | Your detection rules break when log formats change | Use a schema-on-write approach with a robust parser |
Expert advice: Start with three rules and tune them for a week before adding more. Too many rules at once create alert fatigue. Your team will ignore the system if it screams every five minutes. Let the data guide your rule set.
Choosing the Right Tools for 2026
The tooling landscape for log monitoring has matured significantly. You no longer need to build everything from scratch. For most teams, a combination of an open source log shipper, a time-series database, and a commercial SIEM offers the best balance of cost and capability.
If you are running on AWS, consider using S3 access logs with Athena for querying and Lambda for real-time alerting. For Google Cloud users, Cloud Logging paired with BigQuery works well. Self-hosted setups can rely on the ELK stack (Elasticsearch, Logstash, Kibana) or the newer Grafana and Loki combination.
The important thing is to choose tools that your team already knows. Do not introduce a new SIEM that nobody understands. A simple system that gets used every day beats a complex one that sits in a corner.
How to Test Your Monitoring Pipeline
Before you go live, test your setup. Simulate an attack to verify that your alerts fire and your automated responses work. Here is a practical test plan.
First, generate a burst of download requests from a test IP using a script. Use a tool like curl in a loop to request 100 files in 30 seconds. Check that your mass download rule triggers. Then, send a series of requests with a fake user agent string and verify that your user agent anomaly rule catches it.
Next, test your geo-fencing by routing traffic through a VPN in a blocked region. Confirm that the request is either blocked or flagged. Finally, test the response action. If your rule is supposed to block the IP, verify that subsequent requests from that IP are denied.
Run these tests during a maintenance window. Do not test on production traffic during peak hours. Document the results and adjust your thresholds if needed.
Building a Long-Term Log Strategy
Real-time monitoring is not a set-it-and-forget-it project. Your file hosting access logs change as your application evolves. New file types, new user roles, and new integrations all alter the baseline. Schedule a quarterly review of your detection rules.
Also, think about log retention. Real-time monitoring needs hot data, but you also need cold storage for forensics. Keep your logs hot for 30 to 90 days depending on your compliance requirements. Archive everything older than that to a cost-effective object storage bucket. You never know when you will need to trace a breach back to a request from six months ago.
For more on building a comprehensive security posture around your file hosting, check out our guide on top strategies for securing your cloud storage data. And if you are evaluating providers, our comparison of is self-hosted file storage right for your project can help you decide.
Your Logs Are Talking, Are You Listening?
File hosting access logs contain the story of every interaction with your stored data. In 2026, real-time security monitoring is not a luxury. It is a necessity for anyone who manages cloud infrastructure. The setup takes a weekend. The payoff is the ability to detect a breach before it becomes a headline.
Start with your most sensitive buckets. Build your pipeline one step at a time. Test your rules. And then expand from there. Your future self will thank you when an alert catches a bad actor at 2 AM instead of discovering the damage in the morning standup.